2 min read

Governance with nothing to govern

Governance with nothing to govern


Your AI governance project has nothing to govern. That's why it stalled.

An IT lead told me last week how his AI roadmap starts: "step one would be get the governance sorted before we do anything." It's the textbook answer. My industry has been selling it for two years.

Then he told me what happened last time. He bought a third-party governance tool. Then, "due to conflicting priorities", he "never actually got as far as doing very much with that."

That isn't a failure of discipline. It's what happens to governance that has nothing to govern.

In the organisations I met last week, governance with no named business process behind it had no owner, no deadline and no budget. So it waited. Governance tied to one process that matters gets approved.

That's a hard message for my industry. Governance-first has become the default AI offer from managed service providers (MSPs) because it sits right next to what we already sell: security, permissions and policy.


The licences are out, the process work isn't

Last week we held four AI discovery conversations. Every organisation had handed out Copilot licences. Not one had put AI inside a business process. As one IT lead put it: AI is "distributed to the business leaders, but into the processes … we haven't implemented any AI related stuff."

Meanwhile the people with the budget are asking a different question. At a pharmacy group, governance was "a necessary precaution", but the real focus was replacing manual work. At another business the CFO signs, and implementation could happen within about three months if the business value is clear.

IT wants guardrails first. Finance wants outcomes first. A governance-only proposal wins over the person who can't sign and loses the person who can.


Where providers, including us, get it wrong

The market has converged on one message. One large Microsoft consultancy puts it in capitals: "Governance MUST come first." Readiness assessments, oversharing audits and label taxonomies are all useful. None of them tells you which process you're protecting. Without that, you end up where one not-for-profit leader is: "we have a policy, it looks great in paper … we cannot police it."

I'm not throwing stones. We did it ourselves this month. A customer asked us for a focused SharePoint foundation, and our proposal turned it into "a broader Microsoft 365 governance project". Our own apology admitted we'd done it "without first playing our interpretation back to you".

The better conversation starts somewhere else. As one of my team put it in our sales review: "We don't need to bring them AI contracts. We need to go, how's your CRM going?" That same week I built a working business app in two hours for a customer who had never thought of his MSP as someone who solves business-process problems.


What this means for leaders

Governance is a seatbelt. Nobody buys a seatbelt instead of a car.

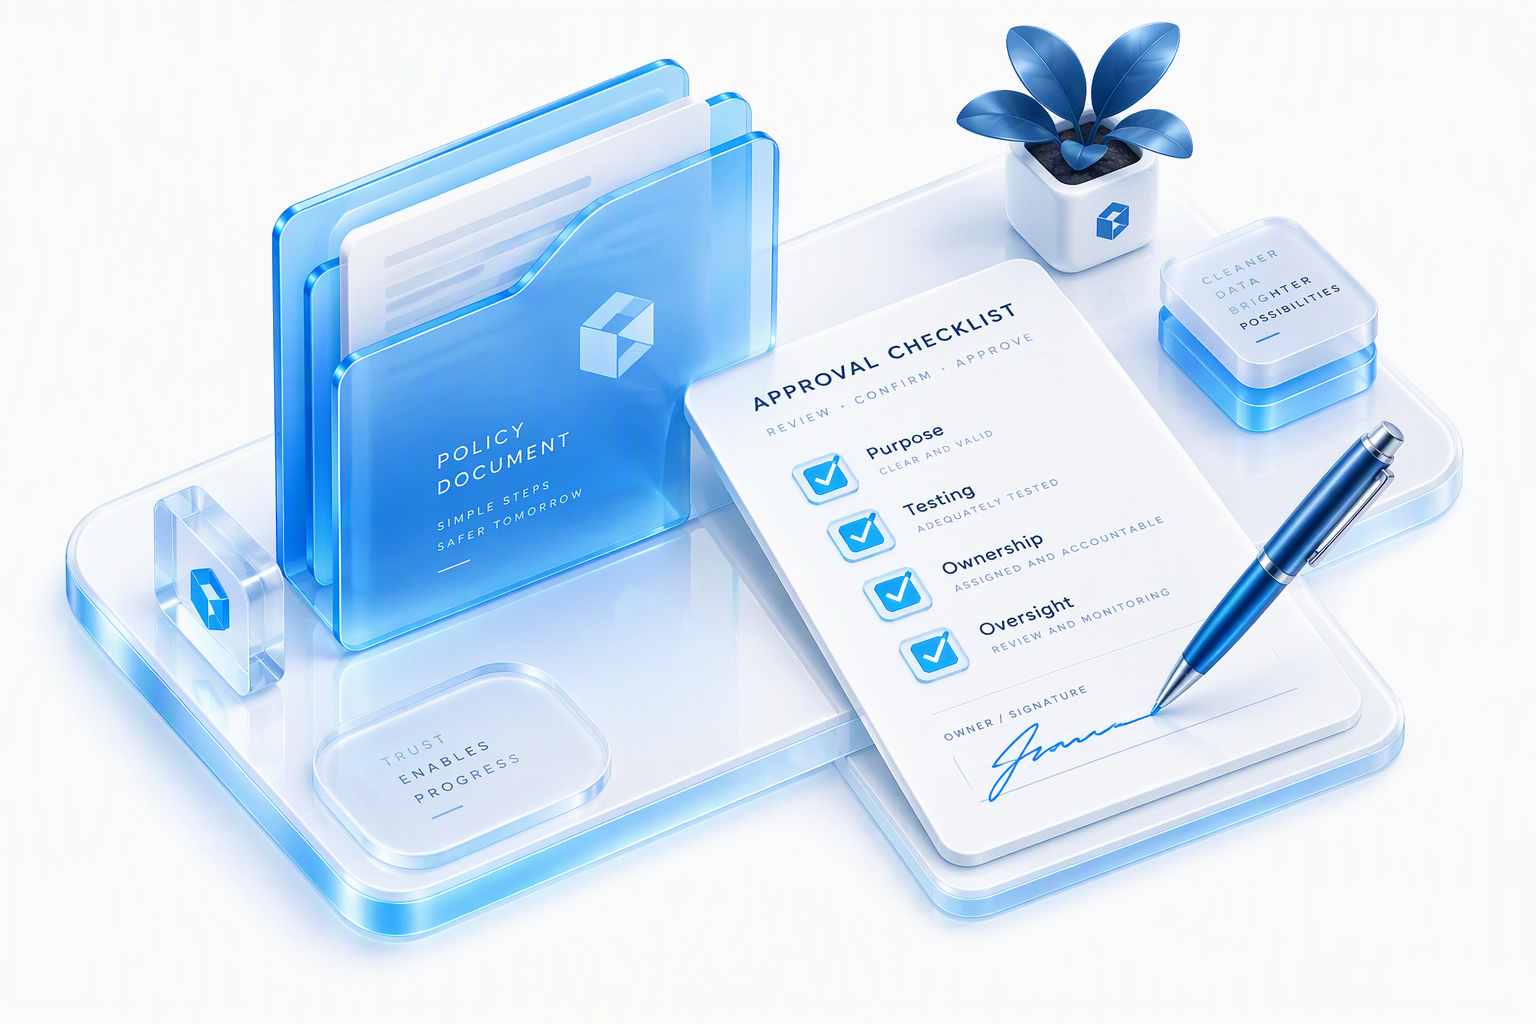
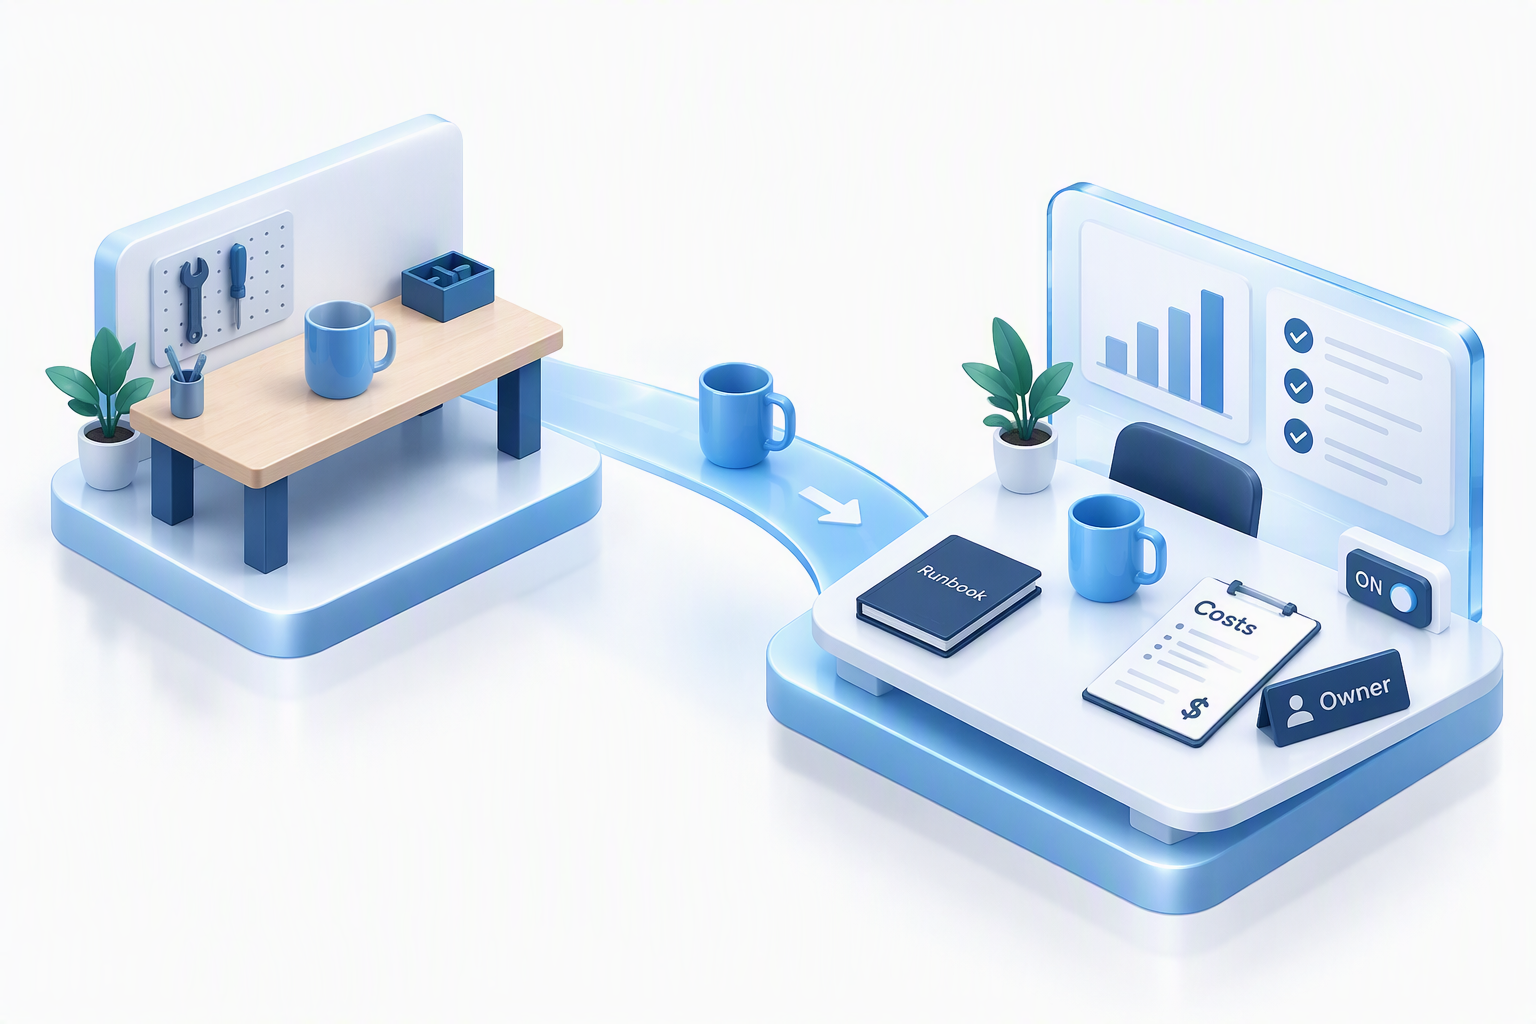
  • Name the process before you fund the guardrails: one workflow, one owner, one measure. Then govern that properly.
  • Make every governance proposal answer one question: what will this let us switch on, and by when?
  • Put the CFO's question and the IT lead's question in the same proposal. Split them and one will lose.
  • Ask your MSP what it has built inside a business process, not just what it has assessed.

Governance done for a live process gets finished. Governance done in the abstract waits for a quieter quarter that never comes.

How to escape the AI pilot trap

1 min read

How to escape the AI pilot trap

Australian organisations have spent the past two years experimenting with artificial intelligence. New tools have appeared at speed, pilots have...

Read More